
Imagine you have a digital document. You want to prove that no one has changed a single comma in it since you signed it. How do you do that without sending the whole file back and forth for comparison? You use a cryptographic hash. In the world of blockchain technology, this isn't just a neat trick; it's the DNA that makes everything trustworthy. Without it, Bitcoin would be nothing more than a shared spreadsheet that anyone could edit.
If you've ever wondered how a decentralized network agrees on the truth without a central bank or government checking the books, the answer lies in these short strings of letters and numbers. This guide breaks down exactly what cryptographic hashing is, why it’s the backbone of blockchain security, and how it protects your transactions from tampering.
The Digital Fingerprint Analogy
Let’s strip away the jargon for a second. Think of a cryptographic hash function as a super-fast, one-way blender. You throw in ingredients-data of any size, whether it’s a single word like "hello" or the entire text of *War and Peace*. The blender spits out a smoothie with a unique flavor profile. That flavor profile is the hash.
Here’s the catch: this blender is magic. If you change even one tiny ingredient-say, swapping an 'e' for an 'a' in "hello"-the resulting smoothie tastes completely different. There is no way to reverse-engineer the original ingredients by tasting the smoothie alone. And crucially, two different sets of ingredients will never produce the exact same taste (at least, not until you find a collision, which we’ll get to later).
In blockchain terms, this "taste" is a fixed-length string of characters. For example, SHA-256 is a cryptographic hash function that produces a 256-bit (32-byte) output, typically represented as a 64-character hexadecimal string. It doesn’t matter if you input 1 byte or 10 gigabytes; the output is always 64 characters long. This consistency allows computers to verify massive amounts of data incredibly quickly.
Why Blockchain Needs Hashing
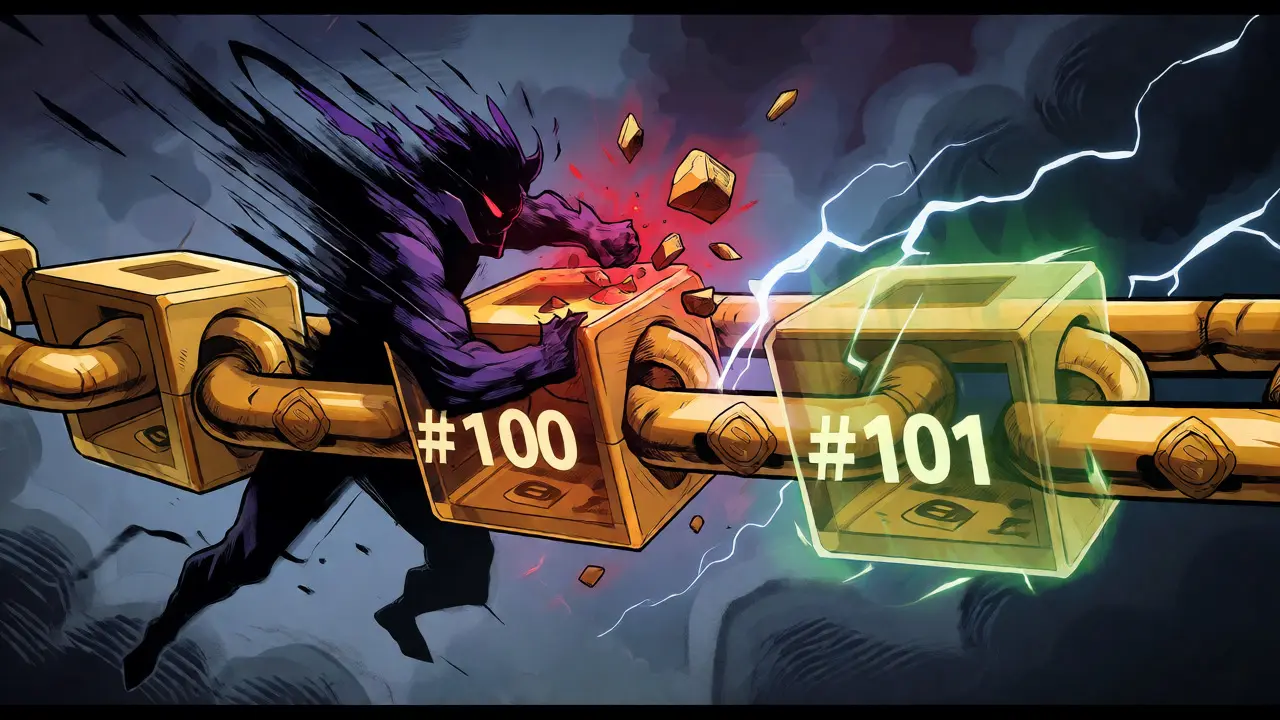
So, why does Bitcoin care about smoothies? Because blockchain is essentially a chain of blocks, and each block contains a list of transactions. But how do you ensure that Block #100 hasn’t been secretly altered after Block #101 was added?
You link them together using hashes. Every block contains:
- The hash of its own transaction data.
- A timestamp.
- The hash of the previous block.
This last point is the game-changer. If someone tries to hack into Block #100 and change a transaction amount from $10 to $10,000, the hash of Block #100 changes instantly. But Block #101 still holds the old hash of Block #100. Now there’s a mismatch. To fix it, the hacker must recalculate the hash of Block #100, then update Block #101 to match, then Block #102, and so on, all the way to the current tip of the chain. Doing this faster than the rest of the network can add new blocks requires immense computing power, making tampering practically impossible.
The Eight Pillars of a Secure Hash
Not just any math function works here. A cryptographic hash function used in blockchain must meet strict criteria. If it fails even one, the security model collapses. Here are the non-negotiables:
- Deterministic: The same input always produces the same output. No randomness allowed.
- Fast Computation: It needs to be quick enough to process thousands of transactions per second but slow enough to deter brute-force attacks.
- Preimage Resistance: Given a hash, you cannot figure out the original input. It’s a one-way street.
- Collision Resistance: It should be computationally infeasible to find two different inputs that produce the same hash.
- Avalanche Effect: A tiny change in input (like flipping one bit) causes a drastic, unpredictable change in the output hash.
- Second Preimage Resistance: Given an input and its hash, it’s hard to find a different input that produces the same hash.
- Puzzle Friendliness: Useful for mining, where finding a specific type of hash requires guessing and checking.
- Fixed Output Length: Always returns a string of the same size, regardless of input size.
Bitcoin uses SHA-256, which stands for Secure Hash Algorithm 256-bit. It’s been battle-tested for over 15 years. Ethereum, on the other hand, historically used Keccak-256 (often called SHA-3), though its architecture has evolved significantly with recent upgrades.
Merkle Trees: Organizing the Chaos
A single block can contain thousands of transactions. Checking each one individually against the block header would be inefficient. Enter the Merkle Tree, a hierarchical data structure that summarizes all transactions in a block.
Imagine pairing up every transaction hash, hashing those pairs together, and repeating the process until you’re left with a single root hash-the Merkle Root. This root goes into the block header.
Why bother? Efficiency. If you only want to verify that your transaction is in a block, you don’t need to download the whole 1MB+ block. You just need the Merkle Root and a small branch of hashes leading to your transaction. This is called Simplified Payment Verification (SPV). It allows lightweight wallets on your phone to verify payments without storing the entire blockchain history.
| Feature | SHA-256 (Bitcoin) | Keccak-256 / SHA-3 (Ethereum legacy) | BLAKE2b (Nano, Polkadot) |
|---|---|---|---|
| Output Size | 256 bits (64 hex chars) | 256 bits (64 hex chars) | Variable (up to 512 bits) |
| Speed (Software) | Moderate | Slower (~15% slower than SHA-2) | Very Fast (1.3x - 1.7x faster than SHA-2) |
| Security Status | Battle-tested, highly secure | Secure, resistant to length extension attacks | Secure, optimized for modern CPUs |
| Primary Use Case | Proof-of-Work Mining | Data Integrity & Address Generation | High-throughput ledgers |
Hashing vs. Encryption: Don’t Mix Them Up
This is the most common confusion among beginners. People hear "crypto" and think of locking things up. But hashing is not encryption.
Encryption is reversible. You lock a message with a key, send it, and the recipient unlocks it with a matching key. You can get the original text back.
Hashing is irreversible. You take a password, hash it, and store the hash. When you log in, the system hashes your entered password and compares it to the stored hash. If they match, you’re in. The system never knows your actual password. In blockchain, we mostly use hashing for integrity checks and mining puzzles, while encryption (via public/private keys) handles ownership and privacy.
The Quantum Elephant in the Room
Is SHA-256 safe forever? Probably not. We have our eyes on quantum computing. Current classical computers would take billions of years to break SHA-256 via brute force. But a sufficiently powerful quantum computer running Grover’s algorithm could theoretically cut that time in half.
However, halving the security level of a 256-bit hash leaves you with 128-bit security, which is still considered robust for the near future. Experts suggest that hybrid approaches-combining traditional hashing with post-quantum algorithms like SPHINCS+-will likely be integrated into blockchains before quantum threats become critical. For now, the energy cost of mining acts as a bigger barrier to attack than quantum math.
Practical Takeaways for Developers and Users
If you’re building on blockchain or just curious about the tech, keep these points in mind:
- Integrity Check: If a file’s hash matches the one on the blockchain, the file hasn’t changed. Period.
- Address Generation: Your Bitcoin address is actually a hashed version of your public key. Shortening it via hashing makes it easier to share and less prone to typing errors.
- Mining Puzzles: Miners aren’t solving complex equations; they’re guessing random numbers (nonces) until they find a hash that starts with a certain number of zeros. It’s a lottery ticket machine powered by electricity.
Cryptographic hashing turns trust from a human problem into a mathematical certainty. It ensures that once data is written to the blockchain, it stays there, unchanged, forever. That’s not marketing fluff; that’s math.
Can I decode a blockchain hash to see the transaction details?
No. Hash functions are one-way. You cannot retrieve the original data from the hash alone. To see transaction details, you must look up the block containing the hash in a blockchain explorer, which stores the full data alongside the hash.
What happens if two transactions have the same hash?
This is called a collision. For SHA-256, collisions are so rare they haven't happened naturally in Bitcoin's history. If it did occur, the network would reject the duplicate because the state wouldn't match, effectively preventing double-spending through consensus rules rather than just the hash itself.
Why does changing one letter change the entire hash?
This is known as the avalanche effect. It ensures that similar inputs produce vastly different outputs. This property prevents attackers from guessing inputs based on patterns in the output, enhancing security.
Is SHA-256 the only hash used in blockchain?
No. While Bitcoin uses SHA-256, Ethereum uses Keccak-256 (SHA-3 variant), and newer chains like Nano or Polkadot often use BLAKE2b for speed. The choice depends on the balance between security, speed, and hardware compatibility required by the specific network.
How does hashing help with privacy?
Hashing hides sensitive information. For instance, passwords are stored as hashes, not plain text. In blockchain, while transaction data is public, the linkage between real-world identities and addresses is obscured, providing pseudonymity rather than total anonymity.
 Cryptocurrency Guides